

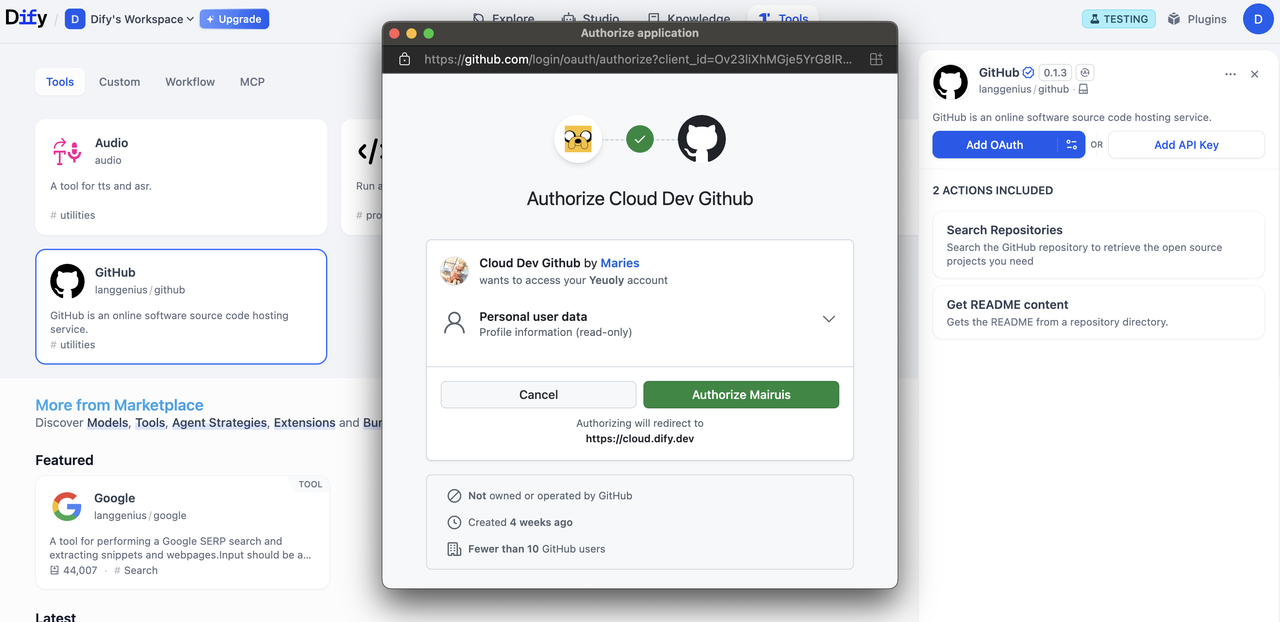
Background
OAuth in Intellos involves two separate flows that developers should understand and design for.Flow 1: OAuth Client Setup (Admin / Developer Flow)
Intellos instance’s admins or developers first need to register an OAuth app at the third-party service as a trusted application. From this, they’ll be able to obtain the necessary credentials to configure the Intellos tool provider as an OAuth client. As an example, here are the steps to setting up an OAuth client for Intellos’s Gmail tool provider:Create a Google Cloud Project
Create a Google Cloud Project
- Go to Google Cloud Console and create a new project, or select existing one
- Enable the required APIs (e.g., Gmail API)
Configure OAuth Consent Screen:
Configure OAuth Consent Screen:
- Navigate to APIs & Services > OAuth consent screen
- Choose External user type for public plugins
- Fill in application name, user support email, and developer contact
- Add authorized domains if needed
- For testing: Add test users in the Test users section
Create OAuth 2.0 Credentials
Create OAuth 2.0 Credentials
- Go to APIs & Services > Credentials
- Click Create Credentials > OAuth 2.0 Client IDs
- Choose Web application type
- A
client_idand aclient_secretwill be generated. Save these as the credentials.
Enter Credentials in Intellos
Enter Credentials in Intellos
Enter the client_id and client_secret on the OAuth Client configuration popup to set up the tool provider as a client.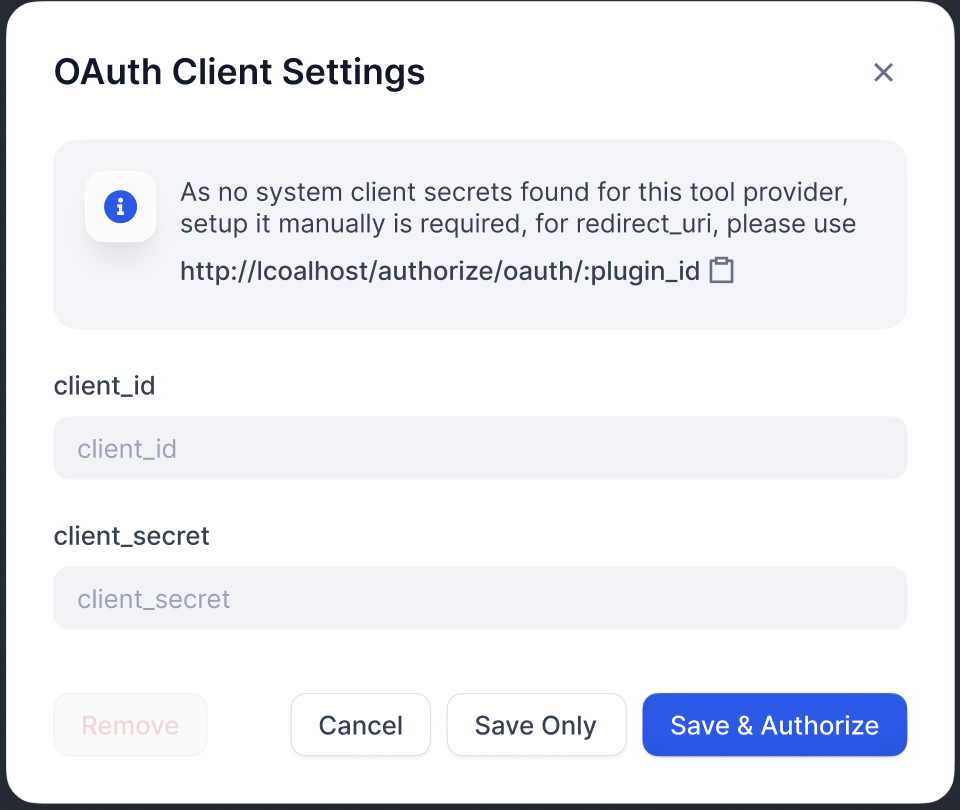
Register the redirect URI generated by Intellos on the Google OAuth Client’s page: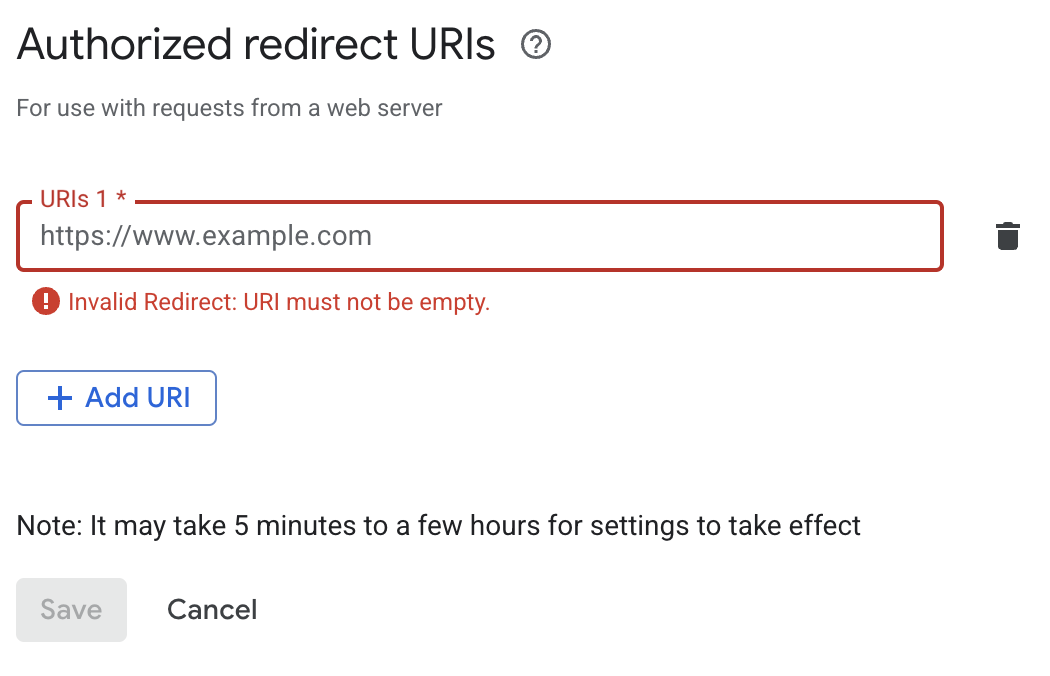
Intellos displays the For self-hosted Intellos, the
redirect_uri in the OAuth Client configuration popup. It usually follows the format:your-dify-domain should be consistent with the CONSOLE_WEB_URL.Flow 2: User Authorization (Intellos User Flow)
After configuring OAuth clients, individual Intellos users can now authorize your plugin to access their personal accounts.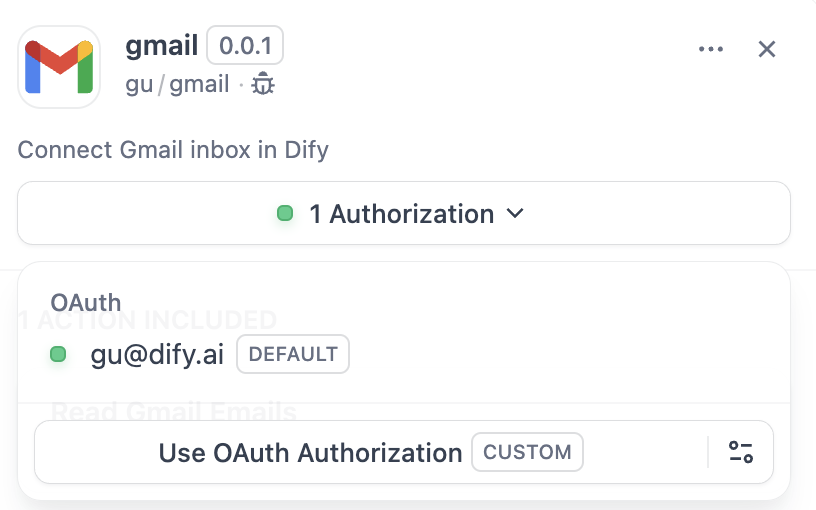
Implementation
1. Define OAuth Schema in Provider Manifest
Theoauth_schema section of the provider manifest definitions tells Intellos what credentials your plugin OAuth needs and what the OAuth flow will produce. Two schemas are required for setting up OAuth:
client_schema
Defines the input for OAuth client setup:gmail.yaml
The
url field links directly to help documentations for the third-party service. This helps confused admins / developers.credentials_schema
Specifies what the user authorization flow produces (Intellos manages these automatically):Include both
oauth_schema and credentials_for_provider to offer OAuth + API key auth options.2. Complete Required OAuth Methods in Tool Provider
Add these imports to where yourToolProvider is implemented:
ToolProvider class must implement these three OAuth methods (taking GmailProvider as an example):
3. Access Tokens in Your Tools
You may use OAuth credentials to make authenticated API calls in yourTool implementation like so:
self.runtime.credentials automatically provides the current user’s tokens. Intellos handles refresh automatically.
For plugins that support both OAuth and API_KEY authentication, you can use self.runtime.credential_type to differentiate between the two authentication types.
4. Specify the Correct Versions
OAuth requires a recent SDK and Intellos version. Pin the plugin SDK inrequirements.txt:
manifest.yaml, add the minimum Intellos version:
Edit this page | Report an issue